
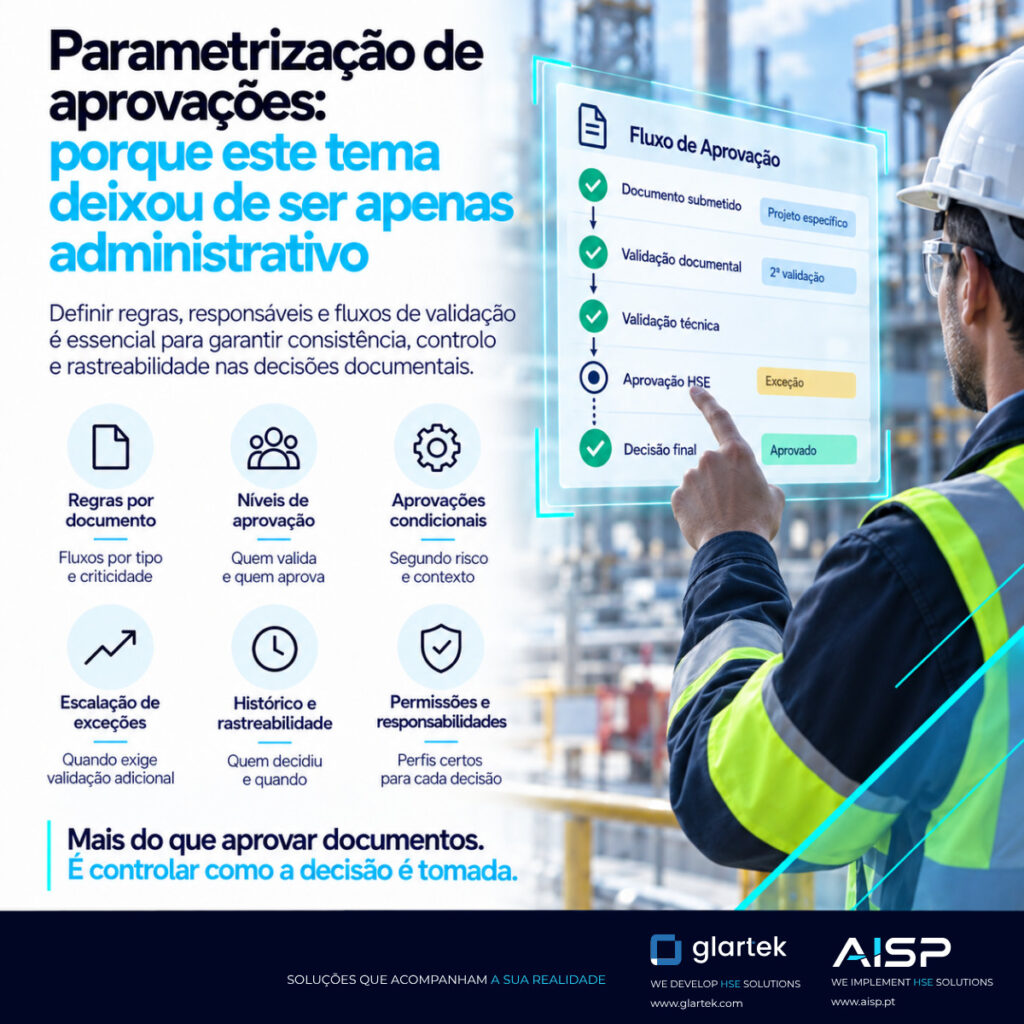
In a simple document process, approval configuration can look like an essentially administrative task: someone submits a document, someone else reviews it and, if it is correct, approves it.
However, this logic quickly falls short when an organisation works with multiple suppliers, workers, equipment, projects, requirements, risk levels and areas of responsibility.
In these contexts, therefore, one question becomes unavoidable:
Who should approve what, under which conditions and based on which rules?
That is precisely why approval configuration is no longer just a workflow issue.
In fact, it is now part of document governance, risk management and operational control itself.
Not all documents should follow the same path
However, one limitation of many traditional document processes is that they apply the same logic to all documents.
The document comes in.
Someone reviews it.
Someone approves or rejects it.
But different types of document may need very different levels of review.
For example, a standard certificate can follow a relatively simple process.
On the other hand, an exception in a fitness certificate, a critical authorisation, a technical equipment document or evidence related to a high risk may require additional validation.
That is why a robust platform must let you configure different workflows depending on the context.
As a result, approval can vary according to:
- document type;
- company;
- worker;
- role;
- activity;
- project;
- client;
- risk level;
- validation result;
- existence of exceptions;
- value or criticality of the process.
The approval logic is therefore no longer one-size-fits-all.
In this way, it reflects the reality of the organisation.
Approving is not just clicking a button
In fact, a document approval is a decision.
And, like any relevant decision, it must come with responsibility, criteria and traceability.
Therefore, a platform must be able to answer questions such as:
- Who reviewed the document?
- Who approved it?
- With which profile or authorisation level?
- Which requirements did they check?
- Was there an exception?
- Did a second validation take place?
- When did the decision happen?
- Did anyone change the document afterwards?
- Did the change require a new approval?
Without this information, the process may look digital, but it remains poorly controlled.
Approval configuration by level of responsibility
The same profiles should not make every decision.
For example, a document team may have the authority to validate certain formal elements.
An HSE manager may need to review a technical exception.
Similarly, a project manager may have to approve client-specific requirements.
In addition, an operations manager may need to validate certain conditions before mobilisation.
That is why a flexible platform must allow different levels of responsibility.
For example:
First level, document validation
Confirmation of data, validity, ownership and mandatory elements.
Second level, technical validation
Review of specific requirements, competences or special conditions.
Third level, operational approval
Confirmation that the evidence provided is sufficient for the context of use.
However, the configuration will naturally depend on each organisation’s reality.
So the key is not to force every process to follow exactly the same model.
Approval configuration with conditional rules
In addition, another important element is the ability to create conditional rules.
Not all documents need to go through every stage.
For example, a platform can allow:
If the document is complete, valid and has no exceptions:
move to standard approval.
Where there is an inconsistency:
send for review.
If it relates to a critical risk:
request a second validation.
Where the document was previously rejected:
send for specific review.
When confidence in the automatic extraction is low:
require human validation.
In this way, this type of logic reduces unnecessary work without losing control.
Approval configuration must keep pace with the organisation
In fact, processes are not static.
For example, a client may introduce a new requirement.
In addition, legislation may change.
An organisation may create a new role.
A project may require a different workflow.
Likewise, a certain document type may come to need additional validation.
If every change depends on complex technical development, document management becomes slow and dependent on the supplier.
Therefore, a new generation of platforms must let you configure and adjust:
- requirements;
- statuses;
- responsible persons;
- approval sequences;
- notifications;
- exceptions;
- escalation rules;
- access levels.
As a result, the more configuration autonomy you have, the faster the platform can keep up with operational reality.
Approval configuration and artificial intelligence
In addition, artificial intelligence can support several stages of the document process.
It can help identify data, classify documents, flag inconsistencies or extract relevant information.
But this capability does not remove the need for approval rules.
In reality, it makes them even more important.
For example, AI can identify an expiry date.
It can recognise an issuing body.
It can also detect a competence.
But the organisation needs to define:
Is that information enough to approve?
Which requirement should the system compare it with?
What confidence level is acceptable?
When should a person validate the result?
Which situations should never receive automatic approval?
Therefore, automation must work within a governance model.
Not outside it.
Exceptions need their own paths
Moreover, document processes are rarely completely linear.
There are exceptions.
For example, a document may be incomplete.
There may be a restriction.
A competence may not match the requirement exactly.
Information may also be contradictory.
In these situations, therefore, the platform must be able to route the case to the right profile.
A generic “pending” status is not enough.
It is important to know:
Waiting for what?
Waiting for whom?
For what reason?
What decision is needed?
This level of detail therefore significantly improves team efficiency.
Traceability of decisions
In addition, a robust approval must leave a history.
This includes:
- submission;
- review;
- changes;
- comments;
- rejections;
- resubmissions;
- approvals;
- responsible persons;
- dates;
- versions.
In fact, this information is important in audits, investigations, certification processes and incident analysis.
But it also matters in day-to-day work.
It shows why someone approved a given document and what information they based that decision on.
Less reliance on individual memory
When nobody has configured the approval workflows, much of the process depends on what people know.
“This type of document goes to that person.”
“For this client, we need a second validation.”
“The HSE team has to look at this case.”
This knowledge may work while teams are small.
But it becomes hard to scale.
When the process itself contains the rules, the platform helps route each situation automatically.
As a result, the organisation depends far less on informal instructions.
Document approval linked to operations
Furthermore, approval should not exist in isolation.
In many contexts, in fact, the result of a document validation can directly affect:
- worker mobilisation;
- access to facilities;
- use of equipment;
- start of activities;
- supplier participation;
- internal authorisations.
That is why approval configuration is increasingly an operational issue.
A document decision can therefore have a direct impact on field work.
More autonomy, more control
A truly configurable platform must let the organisation adjust its processes as needs evolve.
This reduces technology dependence and increases responsiveness.
But autonomy does not mean a lack of governance.
Quite the opposite.
The greater the configuration capability, the more important it is to maintain:
- permissions;
- history;
- change control;
- access profiles;
- traceability.
The organisation must be able to evolve its processes without losing control over what has changed.
From administrative approval to structured decision
A simple comparison shows the change.
Traditional model:
Document → review → approval.
Configured model:
Document → requirement → rule → context → responsible person → validation → decision → traceability.
This shift is what truly brings document management closer to governance and operations.
Because the goal is not just to digitise approval.
It is to ensure that each decision follows the right process, involves the right people and applies the right criteria.
Approval configuration is therefore no longer an administrative feature.
It is an essential part of a robust document process.
See also: Automation in document management and The benefits of automating contractor approval processes.
For international standards on process management and control, visit the International Organization for Standardization (ISO).